Holdfast Cyber crest Holdfast Cyber Secure Today. Defend Tomorrow.
Defense Contract Cybersecurity Readiness

Protect your eligibility for defense work.

Holdfast Cyber helps small and midsize defense manufacturers across Michigan, Ohio, and Indiana identify, close, and maintain DFARS, NIST SP 800-171, and CMMC readiness gaps — without building a full-time compliance team.

~20 questions · under 3 minutes · readiness risk, not an official score

Veteran-owned · Founder-led by Dustin Perkins · Remote-first with on-site support

CISSP CISM CRISC C|CISO ISO/IEC 27001 Lead Auditor U.S. Coast Guard Veteran

Serving Midwest defense manufacturers in Michigan · Ohio · Indiana

The Requirement

The certification timetable changed. Your contract obligations did not.

The Department suspended CMMC Phase II requirements in July 2026 while it reviews the program. Phase I self-assessment requirements remain in place, and existing DFARS safeguarding, NIST SP 800-171, SPRS, and supplier flow-down obligations still affect defense work.

Most midsize defense shops don’t have a CISO. Security work sits with the owner, controller, VP of Ops, and whoever keeps the network alive — often an MSP — absorbing NIST 800-171 on top of a full-time role.

Holdfast Cyber closes that gap without asking you to build a team for it: one accountable senior practitioner and a clear path from contract language to defensible evidence.

Why it matters

Know what your contracts require — and be ready to prove it.

A prime request, solicitation clause, expiring SPRS assessment, or future certification requirement can all expose the same underlying problem: controls that exist informally but cannot be demonstrated with current evidence.

Don’t lose your prime contract flow-downs over an SPRS score.

Who this is for
Services

Three ways to move from uncertainty to defensible readiness

Start with the decision your business needs to make. Every engagement is built on your contracts, systems, people, and actual evidence — never boilerplate with a new logo.

Start here 01

Contract Cyber Readiness Diagnostic

Confirm the applicable requirements, validate scope, test evidence, and receive a defensible baseline with a prioritized action plan.

We work alongside your IT/MSP — clear scope and a Position Report from us; systems and ops stay with them.

02

Evidence-Ready Implementation

Close control gaps, build an accurate SSP and POA&M, strengthen policies, and assemble evidence that matches operations.

Details →
03

Managed Readiness Office

Maintain evidence, review controls, manage corrective actions, and answer customer or assessor requests without a full-time compliance hire.

Details →
The Approach

Three phases, one accountable path

A disciplined engagement model that moves your defense program from an honest starting position to a maintained state of readiness — with defined deliverables at every phase.

01
Assess

Position Report

We interpret the requirement, validate the CUI boundary, test implementation and evidence, and hand you a prioritized roadmap tied to contract and operational risk.

Contract ReviewScope ValidationSPRS BaselinePrioritized Roadmap
02
Implement

Course to Compliance

We close the agreed gaps with your team, align documentation to reality, and establish repeatable operating practices that produce credible evidence.

PoliciesSSP & POA&MControl RemediationOperating Evidence
03
Sustain

Hold Fast

Continuous monitoring, evidence discipline, corrective actions, and recurring reviews keep readiness operating between assessments — and keep your team prepared when an independent assessor or certification body arrives.

Continuous MonitoringEvidence ManagementAudit Support
Partnership

We work with your IT / MSP — we don’t replace them

Most midsize defense shops don’t have a CISO. Security work sits with the owner, controller, VP of Ops, and whoever keeps the network alive (often an MSP). Holdfast is built for that reality.

Holdfast owns

  • Scoping what CUI / contract requirements actually touch in your shop
  • Mapping NIST SP 800-171 / CMMC Level 2 (Self) practices to how you operate
  • Producing the Position Report, prioritized gaps, and a remediation roadmap you can brief to primes or leadership
  • Translating “security speak” into decisions an owner can make
Your IT / MSP owns

  • Day-to-day systems: identity, endpoints, backups, patching, monitoring
  • Implementing technical fixes once priorities are clear
  • Ongoing operations after the Diagnostic

We do together

  • Agree the assessment boundary (what’s in / out)
  • Validate that evidence matches the floor, not just the binder
  • Sequence fixes so shop production and bids don’t stall

We don’t

  • Take over your MSP contract
  • Sell you a tool stack as the “solution”
  • Pretend a PDF binder alone equals SPRS-ready

We work alongside your IT/MSP — clear scope and a Position Report from us; systems and ops stay with them.

Proof of work

What you actually get

Illustrative samples of the artifacts owners and ops leads brief to primes and leadership — not a named client’s files.

See how this would look against your contracts and systems.

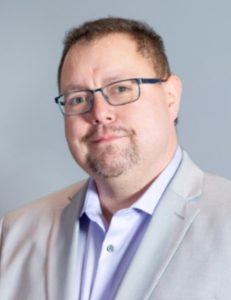
Dustin Perkins, founder of Holdfast Cyber
Dustin Perkins
Founder · USCG Veteran
Leadership

The practitioner who prepares your program stays with you

Holdfast Cyber is led by Dustin Perkins, a career governance, risk, and compliance practitioner with more than fifteen years spanning U.S. Coast Guard port security, CISO and VP-level security roles, and principal GRC consulting across a portfolio of defense and commercial clients.

That track record is the standard your engagement is held to: an 8-for-8 first-time ISO/IEC 27001 certification rate with zero critical findings in prior professional roles. No account handoffs, no call center — Dustin from first call through preparation for an independent assessment.

You'll work with Dustin
Founder Track Record

Prior professional outcomes, applied directly to your engagement

These results were achieved by Dustin Perkins in previous professional roles and are not presented as Holdfast Cyber client history.

8/8
First-time ISO/IEC 27001 certifications, zero critical findings
25+
Client portfolio led as a principal GRC consultant
40%
Reduction in high-severity findings across prior managed programs
15+
Years across port security, CISO roles, and GRC consulting
Field Notes & Tools

Start with the trigger that brought you here

Plain-English guidance for supplier requests, contract pressure, and the first readiness decisions your team needs to make.

Field Note · Updated August 2026

Your prime sent a CMMC letter — what does it actually mean?

Understand what changed, what did not, and how to respond without overstating your position or panic-buying technology.

Read the field note →
Free Checklist · About 10 Minutes

Machine Shop CMMC / SPRS Scope Checklist

Print-ready Yes / No / Unsure worksheet to see what’s in scope before the next prime questionnaire.

Get the checklist →
Free Tool · About 3 Minutes

SPRS Readiness Risk Check

Review 20 high-impact readiness questions, identify your most important evidence gaps, and choose a practical next step.

Check my readiness →
Holdfast Cyber crest

Bring us the contract clause, prime request, or readiness question

We'll help you determine what it requires, where your evidence stands, and the most practical next move. No sales queue and no obligation to continue.

Book a 20-min Scope Review
Secure Today. Defend Tomorrow.